Small businesses face an increasingly complex threat landscape in 2026, with cyberattacks becoming more sophisticated and costly. Network security risk management serves as the foundation for protecting digital assets, ensuring business continuity, and maintaining customer trust. For companies in Lethbridge and beyond, implementing a structured approach to identifying, assessing, and mitigating network vulnerabilities is no longer optional but essential for survival in today's interconnected business environment.
Understanding Network Security Risk Management Fundamentals
Network security risk management is the systematic process of identifying potential threats to your IT infrastructure, evaluating their likelihood and impact, and implementing controls to minimize damage. This discipline combines technical safeguards with strategic planning to create a resilient defense against both external attacks and internal vulnerabilities.
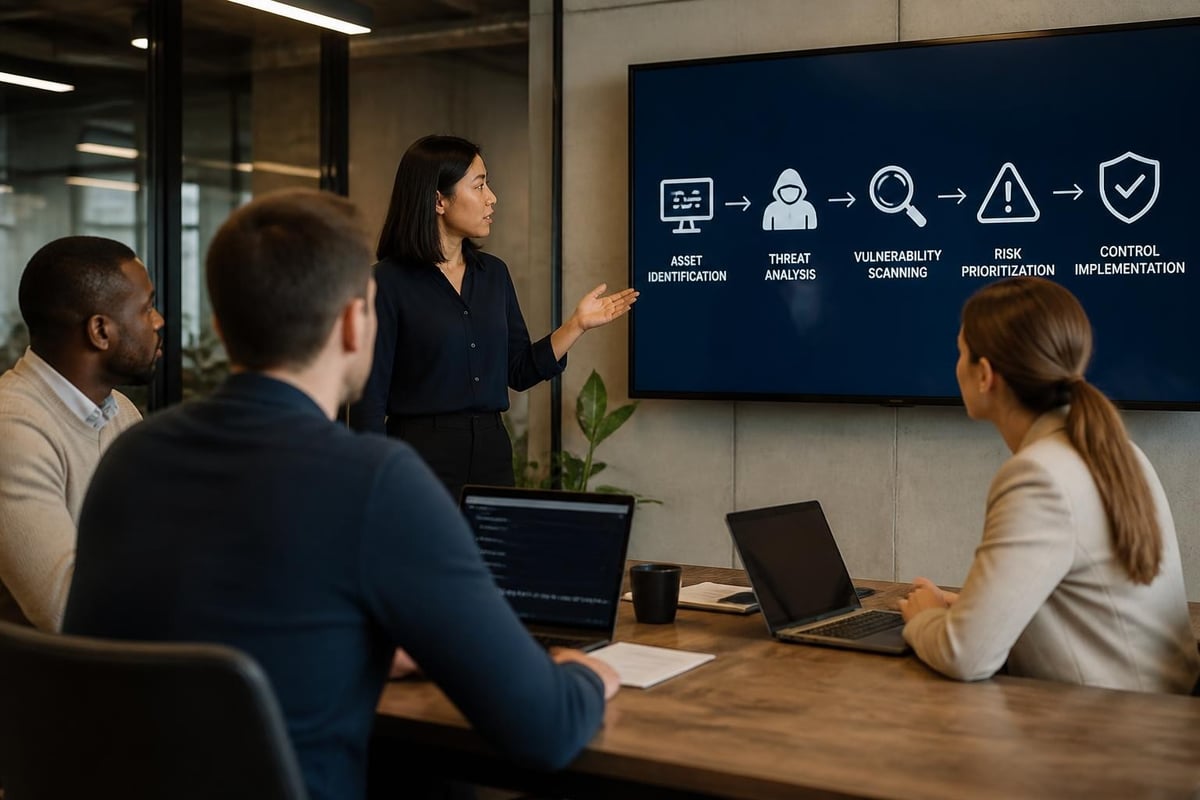
The core components include asset inventory, threat identification, vulnerability assessment, risk analysis, and control implementation. Each element builds upon the previous one to create a comprehensive security posture that adapts to emerging threats while supporting business operations.
Key Components of Risk Assessment
A thorough risk assessment begins with cataloging all network assets, from servers and workstations to routers and cloud services. Understanding what needs protection provides the foundation for everything that follows.
Critical assessment elements include:
- Network topology mapping and device inventory
- Data classification based on sensitivity and regulatory requirements
- User access patterns and privilege levels
- Third-party connections and vendor access points
- Historical incident data and near-miss events
Once you have visibility into your assets, the next step involves identifying threats specific to your environment. Small businesses often face different threat profiles than enterprises, with limited resources making them attractive targets for ransomware and business email compromise attacks.
Implementing Effective Risk Management Frameworks
Several established frameworks provide structured approaches to network security risk management. The NIST Cybersecurity Framework offers a voluntary standard that many organizations find accessible and practical for network infrastructure protection.
The framework organizes security activities into five core functions: Identify, Protect, Detect, Respond, and Recover. This structure helps businesses of all sizes create comprehensive security programs without requiring massive security teams or budgets.
| Framework | Best For | Key Strength | Implementation Complexity |
|---|---|---|---|
| NIST CSF | General business use | Flexibility and scalability | Moderate |
| CIS Controls | Small to medium businesses | Prioritized actions | Low to Moderate |
| ISO 27001 | Organizations needing certification | Comprehensive coverage | High |
| COBIT | IT governance focus | Business alignment | High |
Selecting the Right Framework for Your Organization
Choosing a framework depends on your industry, regulatory requirements, and organizational maturity. Small businesses often benefit from starting with the CIS Controls, which provide prioritized implementation guidance based on the most common attack vectors.
The beauty of these frameworks lies in their adaptability. You don't need to implement every control immediately. Instead, focus on quick wins that address your highest risks first. This phased approach makes network security risk management achievable even with limited resources.
Building a Comprehensive Risk Mitigation Strategy
Effective mitigation requires layering multiple security controls to create defense in depth. No single technology or practice provides complete protection, but combining complementary approaches significantly reduces your attack surface.
Essential mitigation layers include:
- Perimeter security through firewalls and intrusion prevention systems
- Endpoint protection with antivirus, anti-malware, and EDR solutions
- Network segmentation to limit lateral movement during breaches
- Access controls using least privilege and multi-factor authentication
- Encryption for data at rest and in transit
- Patch management to eliminate known vulnerabilities
- Security awareness training to address the human element
Regular vulnerability assessments help identify gaps in your defenses before attackers exploit them. Automated scanning tools can monitor your network continuously, flagging misconfigurations and unpatched systems that create unnecessary risk.
Prioritizing Risk Mitigation Efforts
Not all risks deserve equal attention. Risk prioritization considers both likelihood and potential impact to determine where to invest limited security resources. A high-probability, high-impact threat like ransomware demands immediate action, while unlikely scenarios with minimal consequences can wait.
Creating a risk register helps track identified risks, their ratings, and mitigation status. This living document becomes your roadmap for security improvements and demonstrates due diligence to stakeholders, insurers, and regulators.
Network Monitoring and Continuous Improvement
Network security risk management never reaches completion. New threats emerge daily, and your network evolves with business needs. Continuous monitoring and validation provide the visibility needed to maintain security in dynamic environments.
Security Information and Event Management (SIEM) systems aggregate logs from across your infrastructure, correlating events to detect suspicious patterns. For small businesses, managed security service providers can deliver enterprise-grade monitoring without requiring internal expertise or 24/7 staffing.
Establishing Baseline Behavior
Effective monitoring starts with understanding normal network behavior. What applications generate the most traffic? When do employees typically access systems? What external connections are legitimate business activities? Baseline patterns help security tools distinguish between routine operations and potential threats.
Best practices for network security monitoring emphasize the importance of comprehensive audits to identify security gaps in your infrastructure. Regular testing ensures your controls function as intended and adapt to changing threat landscapes.
Monitoring should cover:
- Network traffic patterns and anomalies
- Failed login attempts and privilege escalation
- Configuration changes to critical systems
- Data exfiltration attempts
- Malware signatures and behavior indicators
- Compliance with security policies
Incident Response Planning and Recovery
Despite best efforts, security incidents will occur. The difference between minor disruptions and catastrophic breaches often comes down to preparation. A well-designed incident response plan enables rapid containment, minimizing damage and recovery time.
Your plan should define roles and responsibilities, communication protocols, and step-by-step procedures for common scenarios. Regular tabletop exercises test these procedures in controlled environments, revealing gaps before real incidents create chaos.
| Response Phase | Key Activities | Success Metrics |
|---|---|---|
| Preparation | Plan development, tool deployment, training | Team readiness, drill performance |
| Detection | Monitoring, alert triage, initial assessment | Time to detection, false positive rate |
| Containment | Isolation, threat elimination, evidence preservation | Time to containment, spread limitation |
| Recovery | System restoration, validation, monitoring | Recovery time objective achievement |
| Lessons Learned | Incident review, plan updates, control improvements | Implementation of recommendations |
Data Backup and Business Continuity
Recovery capabilities form the last line of defense in network security risk management. Backing up data regularly and testing restoration procedures ensures business continuity even when prevention and detection fail.
The 3-2-1 backup rule remains relevant in 2026: maintain three copies of critical data on two different media types, with one copy stored offsite. Cloud-based backup solutions offer automated, encrypted storage that protects against both local disasters and ransomware attacks.
Addressing Human Factors in Risk Management
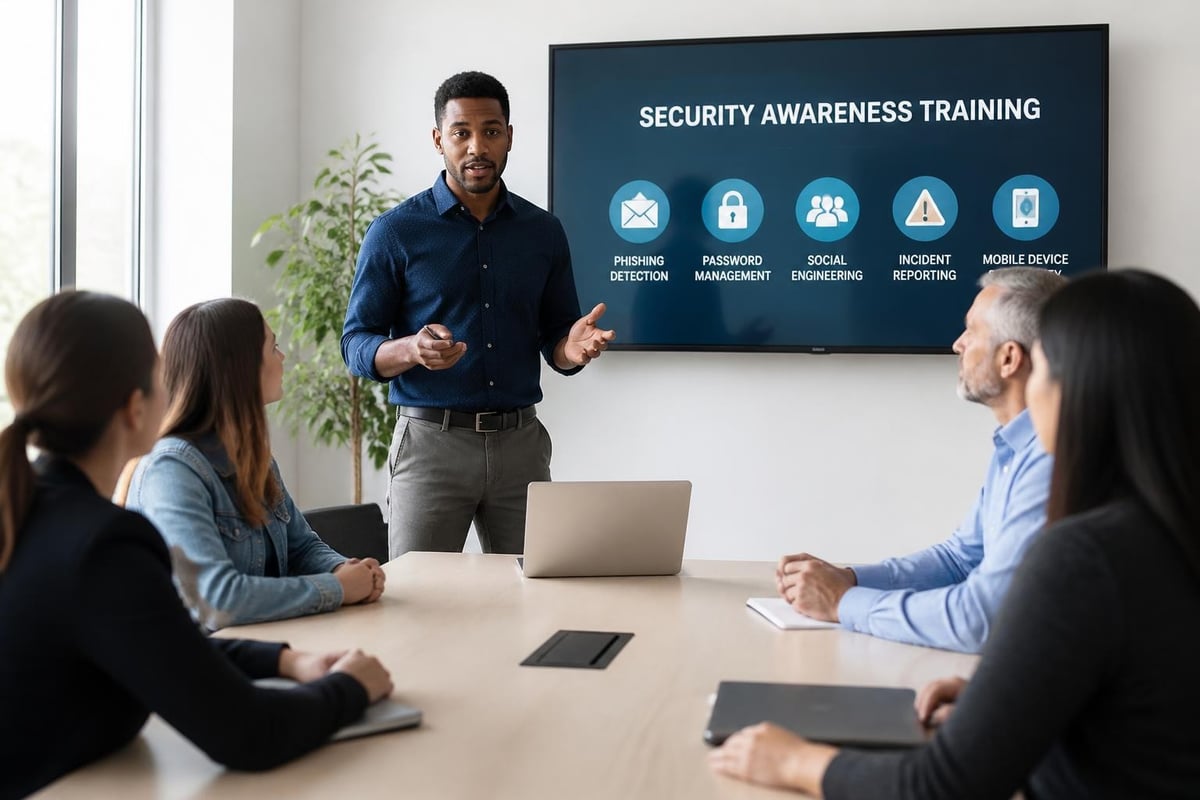
Technology alone cannot secure networks. People create, operate, and defend systems, making human factors central to effective network security risk management. Security awareness training transforms employees from vulnerabilities into active defenders.
Training programs should cover phishing recognition, password hygiene, physical security, and incident reporting. Regular simulations help reinforce lessons and identify individuals who need additional support. Making security part of company culture rather than IT's responsibility alone significantly reduces risk.
Managing Insider Threats
Not all threats come from external attackers. Insider threats, whether malicious or accidental, account for a significant portion of security incidents. Network security risk management must address both intentional data theft and unintentional exposure through negligence.
Access controls, activity monitoring, and clear acceptable use policies help manage insider risk. Regular access reviews ensure employees only retain privileges necessary for current responsibilities. Departing employees should have access revoked immediately to prevent post-employment incidents.
Vendor and Third-Party Risk Management
Modern businesses rely on numerous vendors and service providers, each representing a potential entry point for attackers. Supply chain attacks have increased dramatically, making third-party risk assessment a critical component of comprehensive network security risk management.
Before granting network access to vendors, evaluate their security practices through questionnaires, audits, or certifications. Contractual agreements should specify security requirements, incident notification timelines, and liability for breaches originating from vendor systems.
Third-party risk controls include:
- Vendor security assessments before onboarding
- Network segmentation for vendor access
- Monitoring of vendor activity within your environment
- Regular re-evaluation of vendor security posture
- Contractual security requirements and audit rights
- Incident response coordination procedures
Compliance and Regulatory Considerations
Industry regulations and data protection laws increasingly mandate specific security controls and risk management practices. Organizations handling healthcare information must comply with HIPAA, while those processing credit cards follow PCI DSS requirements. Canadian businesses face PIPEDA obligations for personal information protection.
Compliance frameworks often align with security best practices, making regulatory requirements a useful guide for network security risk management even when not legally obligated. Documentation, regular audits, and control testing satisfy both security needs and compliance requirements.
Documenting Your Security Program
Comprehensive documentation demonstrates due diligence and supports compliance efforts. Policies define what should happen, procedures explain how to do it, and records prove you followed through. This documentation protects your organization legally and operationally.
Key documents include acceptable use policies, incident response plans, disaster recovery procedures, access control matrices, and security awareness training records. Regular reviews keep documentation current as technologies and threats evolve.
Leveraging Managed Services for Enhanced Security
Small businesses often lack the resources to staff comprehensive security programs internally. Managed IT service providers deliver enterprise-level security capabilities at predictable costs, making advanced network security risk management accessible to organizations of all sizes.
Understanding network security management challenges helps businesses recognize when external expertise provides value. Managed services combine technology, monitoring, and expertise to address the full spectrum of network risks.
Fixed-rate pricing models eliminate the unpredictability of security costs while ensuring continuous protection. This approach allows businesses to focus on core activities while security professionals handle threat monitoring, vulnerability management, and incident response.
Effective network security risk management requires combining technical controls, strategic planning, and ongoing vigilance to protect your IT infrastructure from evolving threats. Small businesses in Lethbridge can implement enterprise-grade security without building internal security teams by partnering with experienced managed service providers. Delphi Systems Inc. specializes in maintaining peak network operation for small businesses through comprehensive cybersecurity, monitoring, and IT support services with transparent, fixed-rate pricing that supports business growth while ensuring robust protection.

