Small businesses face an evolving landscape of cyber threats that can compromise their operations, customer data, and financial stability. Understanding network security risks has become essential for organizations of all sizes, particularly as digital transformation accelerates and remote work expands the attack surface. For businesses in Lethbridge and surrounding areas, recognizing these vulnerabilities represents the first step toward building a resilient IT infrastructure that protects critical assets while enabling growth and productivity.
The Expanding Threat Landscape in 2026
Network security risks have grown more sophisticated and diverse throughout 2026. According to ENISA’s Threat Landscape 2025, organizations across the European Union experienced 4,875 documented incidents between mid-2024 and mid-2025, with exploited vulnerabilities and zero-day attacks representing primary attack vectors.
The threat environment now encompasses traditional malware alongside emerging challenges like AI-powered social engineering, supply chain compromises, and cryptographic failures. Small businesses often assume they are too insignificant to attract attention from cybercriminals, yet this misconception leaves them vulnerable to automated attacks and opportunistic threat actors scanning for weaknesses across thousands of networks simultaneously.
Modern Attack Vectors Targeting Business Networks
Today's attackers leverage multiple entry points to compromise business networks:
- Phishing and social engineering campaigns that exploit human psychology to gain credentials
- Unpatched vulnerabilities in software, firmware, and operating systems
- Misconfigured cloud services exposing sensitive data to public access
- Compromised third-party vendors introducing malware through trusted relationships
- Inadequately secured IoT devices creating backdoors into corporate networks
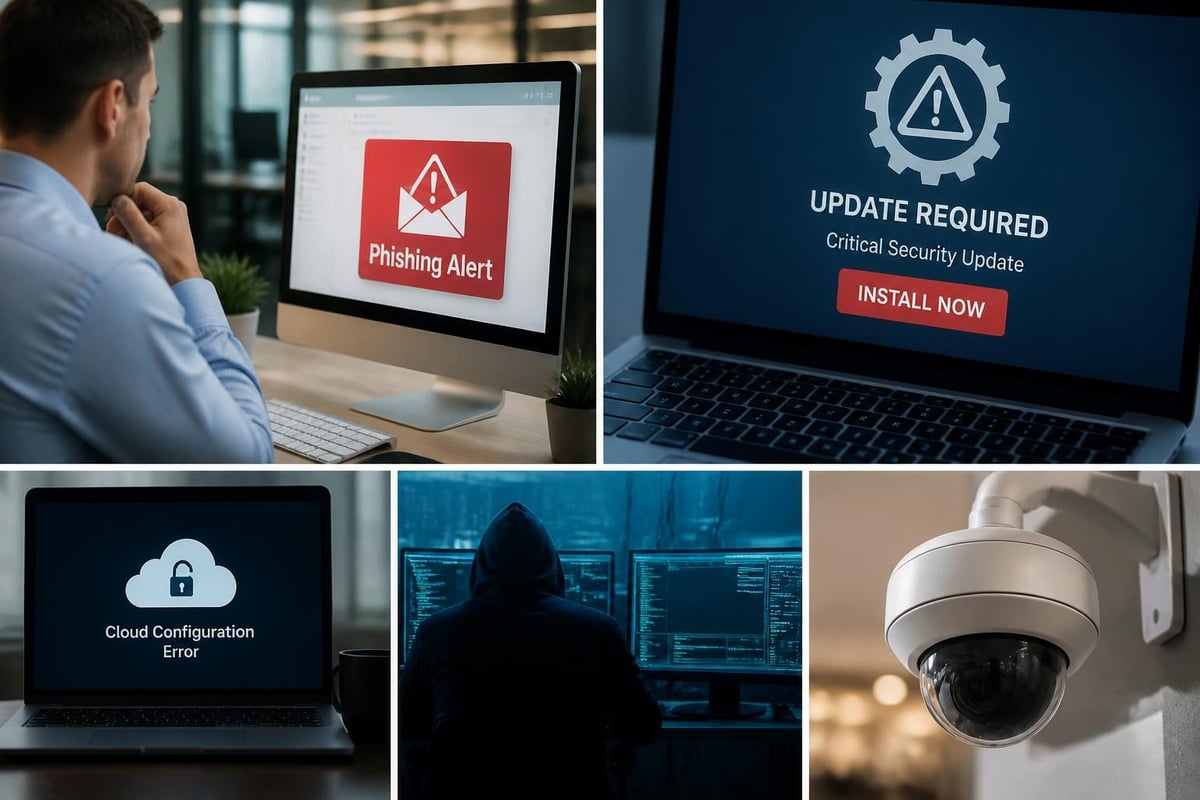
The Palo Alto Networks Unit 42 Incident Response Report 2025 reveals that cloud misconfigurations and network intrusions continue to dominate incident response engagements, with insider threats playing an increasingly significant role in security breaches.
Critical Vulnerabilities Affecting Small Business Networks
Network security risks manifest through specific technical vulnerabilities that attackers actively exploit. Understanding these weaknesses helps organizations prioritize remediation efforts and allocate security resources effectively.
Cryptographic Failures and Insecure Configurations
Research from the Center for Internet Security identifies cryptographic failures as one of the top external network risks discovered through network scanning. Many organizations continue operating outdated encryption protocols, expired SSL/TLS certificates, and weak cipher suites that allow attackers to intercept or manipulate data in transit.
Common cryptographic vulnerabilities include:
- Deprecated TLS 1.0 and 1.1 protocols still accepting connections
- Self-signed certificates triggering browser warnings but accepted by users
- Weak key lengths insufficient for modern computational attacks
- Hardcoded credentials embedded in configuration files or source code
Insecure configurations extend beyond encryption. Default administrative passwords, unnecessary open ports, overly permissive firewall rules, and disabled security logging create opportunities for unauthorized access and undetected compromise.
Web Application Security Gaps
The OWASP Top 10: 2025 outlines critical web application security risks that directly impact network security. Broken access control tops the list, allowing attackers to bypass authorization and access restricted functionality or data. Security misconfigurations, injection flaws, and vulnerable components represent persistent challenges that threat actors routinely exploit.
For businesses running customer portals, e-commerce platforms, or cloud-based applications, these vulnerabilities create direct pathways into internal networks. A compromised web application can serve as a launching point for lateral movement across the corporate network, data exfiltration, or ransomware deployment.
| Vulnerability Type | Business Impact | Mitigation Priority |
|---|---|---|
| Broken Access Control | Unauthorized data access, privilege escalation | Critical |
| Cryptographic Failures | Data breaches, compliance violations | High |
| Injection Attacks | Database compromise, system takeover | Critical |
| Security Misconfiguration | Expanded attack surface, information disclosure | High |
| Vulnerable Components | Known exploit availability | High |
Supply Chain and Third-Party Network Security Risks
Modern businesses rely on interconnected ecosystems of vendors, service providers, and technology partners. These relationships introduce network security risks that extend beyond the organization's direct control yet significantly impact overall security posture.
Software Supply Chain Vulnerabilities
Supply chain attacks have increased in frequency and sophistication. Attackers compromise software vendors or update mechanisms to distribute malware to downstream customers. The CERT-EU Threat Landscape Report 2025 emphasizes how supply-chain attacks and vulnerability exploitation targeting internet-facing systems have emerged as major risks across European organizations.
When a business installs software updates, integrates third-party APIs, or deploys vendor-managed solutions, they inherit the security practices of those external parties. A single compromised vendor can affect hundreds or thousands of downstream customers simultaneously.
Supply chain risk factors:
- Limited visibility into vendor security practices
- Delayed notification of security incidents affecting vendor products
- Dependency on vendor patches for critical vulnerability remediation
- Shared credentials or network access granted to external service providers
- Inadequate vendor security requirements in procurement contracts
IoT and Edge Device Security Challenges
The proliferation of Internet of Things devices and edge computing infrastructure has expanded the network perimeter while introducing devices with limited security capabilities. Smart thermostats, security cameras, printers, and specialized equipment often lack robust authentication, encryption, or update mechanisms.
These devices frequently operate with default credentials, unpatched firmware, and minimal security controls. According to NIST guidance on trusted IoT device network-layer onboarding, organizations must implement secure onboarding processes and lifecycle management to mitigate risks associated with IoT devices connecting to corporate networks.
Securing the Expanding Network Perimeter
Small businesses deploying IoT devices should establish network segmentation to isolate these endpoints from critical business systems. Creating separate VLANs for IoT traffic prevents a compromised smart device from providing access to sensitive data or core infrastructure.
Additional protective measures include:
- Changing all default passwords before deployment
- Disabling unnecessary services and ports on IoT devices
- Implementing network access control to authenticate devices before granting connectivity
- Establishing automated inventory management to track all connected endpoints
- Scheduling regular firmware updates and end-of-life replacement planning
Emerging Risks from AI and Automation
The integration of artificial intelligence into both business operations and cyber attacks represents one of the most significant shifts in network security risks. Deloitte’s Midyear Cyber Threat Trends 2025 highlights AI-enabled threats, deepfakes, and modular attack tools as emerging challenges requiring new defensive approaches.
Attackers now leverage AI to automate reconnaissance, craft convincing phishing messages, identify vulnerabilities faster, and adapt attack techniques in real-time based on defensive responses. This acceleration compresses the time window organizations have to detect and respond to threats.
Conversely, businesses can deploy AI-powered security tools for threat detection, behavioral analysis, and automated response. Machine learning algorithms identify anomalous network traffic patterns, unusual user behavior, and potential indicators of compromise that might escape human analysts.
Implementing a Risk-Based Security Framework
Addressing network security risks requires a structured, prioritized approach rather than reactive responses to individual threats. The NIST Cybersecurity Framework 2.0, released in February 2024, provides comprehensive guidance for identifying, assessing, prioritizing, and communicating cybersecurity risks across the organization.
This framework organizes security activities into six core functions:
- Govern: Establish cybersecurity risk management strategy and oversight
- Identify: Understand assets, risks, and vulnerabilities
- Protect: Implement safeguards to ensure critical service delivery
- Detect: Develop capabilities to discover cybersecurity events
- Respond: Take action when security incidents occur
- Recover: Restore capabilities impaired during incidents
Risk Assessment and Prioritization
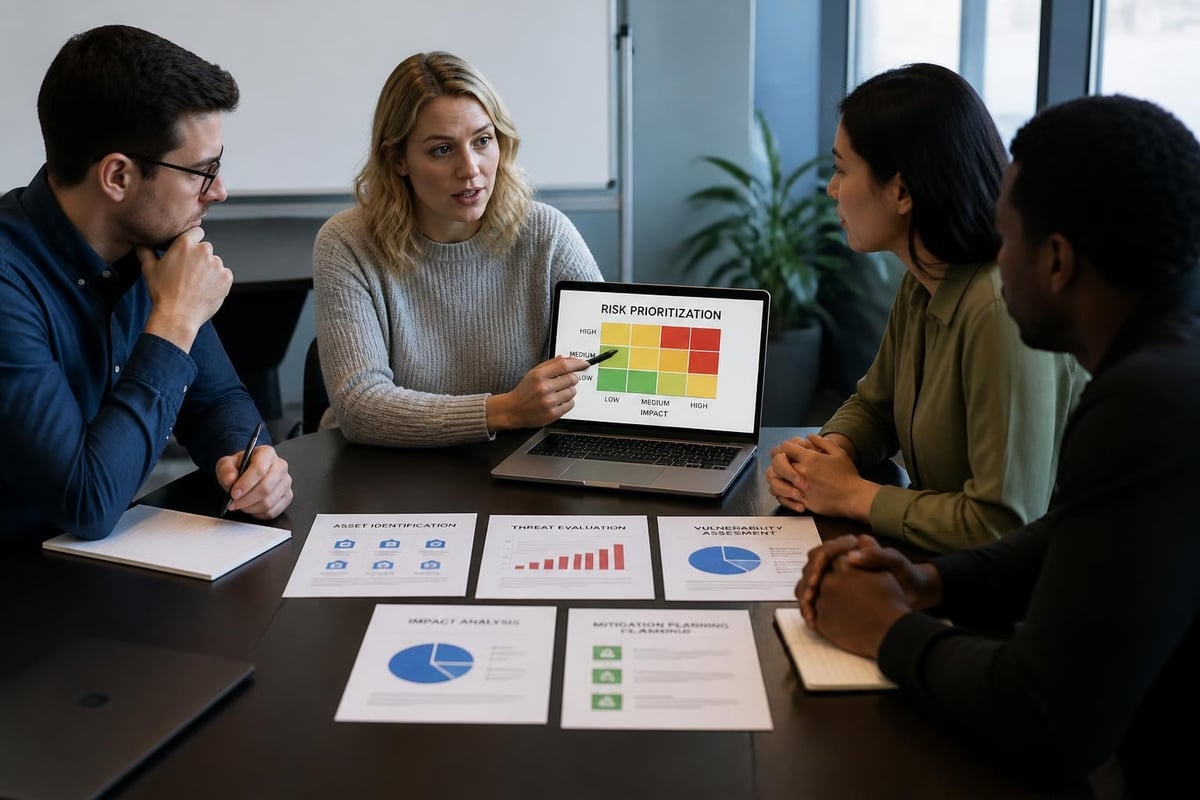
Effective security begins with understanding which assets require the strongest protection and which vulnerabilities pose the greatest danger. Small businesses should conduct regular risk assessments that inventory critical systems, evaluate potential threats, and prioritize remediation based on likelihood and impact.
| Asset Category | Typical Risk Level | Protection Priority |
|---|---|---|
| Customer databases | High | Critical |
| Financial systems | High | Critical |
| Email infrastructure | Medium-High | High |
| Employee workstations | Medium | Medium |
| Guest WiFi networks | Low-Medium | Low |
This prioritization ensures limited security resources focus on protecting the most valuable assets and addressing vulnerabilities that present the greatest business risk.
Proactive Defense Strategies for Small Businesses
Moving beyond reactive security toward proactive defense requires implementing multiple layers of protection that address network security risks before exploitation occurs.
Network Segmentation and Access Control
Dividing the network into logical segments limits lateral movement if attackers breach the perimeter. Separating guest networks, IoT devices, employee workstations, and server infrastructure creates security boundaries that contain compromises and prevent widespread damage.
Effective segmentation strategies include:
- Implementing VLANs to separate traffic by function or security level
- Deploying firewalls between network segments with explicit allow-list rules
- Requiring multi-factor authentication for access to sensitive systems
- Establishing just-in-time administrative access that expires automatically
- Monitoring east-west traffic between internal network segments
Continuous Monitoring and Threat Detection
Traditional perimeter-focused security proves insufficient against modern threats that bypass firewalls through phishing, compromised credentials, or supply chain attacks. Continuous monitoring of network traffic, system logs, and user behavior identifies suspicious activity regardless of how attackers gained initial access.
Small businesses benefit from managed security services that provide 24/7 monitoring, threat intelligence, and expert analysis without requiring dedicated in-house security staff. Automated alerting for configuration changes, failed authentication attempts, unusual data transfers, or connections to known malicious IP addresses enables rapid response before minor incidents escalate into major breaches.
Data Protection and Recovery Planning
While prevention remains ideal, comprehensive security acknowledges that determined attackers may eventually succeed. Data backup and disaster recovery planning mitigates network security risks by ensuring business continuity even after successful attacks.
Backup Best Practices
Ransomware attacks specifically target backup systems to force payment by eliminating recovery options. The 3-2-1 backup rule provides resilient protection: maintain three copies of data, store them on two different media types, and keep one copy offsite or offline.
Critical backup considerations:
- Test restoration procedures regularly to verify backup integrity
- Implement immutable backups that prevent deletion or modification
- Encrypt backup data both in transit and at rest
- Maintain air-gapped or offline backups disconnected from production networks
- Document recovery time objectives and recovery point objectives for critical systems
Employee Training and Security Awareness
Technology alone cannot eliminate network security risks when human factors remain the weakest link. Employees who unknowingly click phishing links, use weak passwords, or mishandle sensitive data create vulnerabilities that attackers readily exploit.
Ongoing security awareness training transforms employees from liabilities into active defenders. Regular training should cover:
- Recognizing phishing emails and suspicious communications
- Creating strong, unique passwords and using password managers
- Reporting security incidents promptly without fear of punishment
- Handling sensitive data according to classification policies
- Securing remote work environments and personal devices
Simulated phishing exercises measure awareness effectiveness and identify employees requiring additional training. These exercises should educate rather than punish, fostering a security-conscious culture throughout the organization.
Compliance and Regulatory Considerations
Many industries face regulatory requirements that mandate specific security controls and risk management practices. Payment card processing requires PCI DSS compliance, healthcare organizations must satisfy HIPAA requirements, and businesses handling certain customer data may face provincial or federal privacy obligations.
Understanding applicable regulations helps organizations avoid penalties while improving overall security posture. Compliance frameworks typically require documented policies, regular security assessments, encryption of sensitive data, access controls, and incident response planning-all practices that directly reduce network security risks.
Vendor Management and Due Diligence
Selecting technology vendors and service providers requires evaluating their security practices alongside functional capabilities and cost. Third-party security questionnaires, SOC 2 audit reports, and security certifications provide insight into vendor risk management maturity.
Contractual protections should address data ownership, breach notification timelines, liability limitations, and security incident cooperation. Service level agreements must define availability requirements, maintenance windows, and support response times for security-related issues.
Regular vendor reviews ensure ongoing compliance with security requirements as threats evolve and business needs change. Vendors who demonstrate commitment to security through transparent communication, proactive patching, and documented incident response planning present lower risk than those treating security as an afterthought.
Building Long-Term Security Resilience
Addressing network security risks represents an ongoing process rather than a one-time project. Threat landscapes shift, technologies evolve, businesses grow, and new vulnerabilities emerge constantly. Organizations that embed security into their culture, processes, and technology decisions build resilience that adapts to changing circumstances.
Small businesses in Lethbridge and surrounding areas face the same sophisticated threats targeting large enterprises, yet typically operate with fewer dedicated security resources. This reality makes strategic planning, risk prioritization, and expert partnership essential for maintaining secure, productive IT infrastructure that supports business objectives while protecting against evolving threats.
Network security risks continue evolving in scope and sophistication, requiring businesses to implement layered defenses, maintain vigilant monitoring, and foster security-aware cultures. Small businesses need not face these challenges alone or build comprehensive security programs from scratch. Delphi Systems Inc. provides managed IT services throughout Lethbridge and surrounding areas, delivering expert cybersecurity, network monitoring, data backup, and IT support that keeps your infrastructure secure and operating at peak performance. With fixed-rate pricing and comprehensive service coverage, we handle the complexities of network security so you can focus on growing your business with confidence.

