Small businesses face an increasingly hostile digital landscape in 2026. Cyberattacks have grown more sophisticated, targeting organizations regardless of size, and the consequences of a security breach can be devastating. For companies in Lethbridge and across Canada, the challenge isn't just recognizing the threat but implementing comprehensive protection without draining internal resources. Managed IT security provides a solution by delivering enterprise-grade protection through specialized providers who monitor, defend, and respond to threats around the clock. This approach transforms security from a reactive burden into a proactive business advantage, allowing small businesses to compete confidently while experts handle the technical complexity.
Understanding Managed IT Security Services
Managed IT security represents a fundamental shift from traditional break-fix approaches. Rather than waiting for incidents to occur, this model emphasizes continuous monitoring, proactive threat hunting, and rapid response capabilities delivered by external security specialists.
The service typically encompasses multiple protection layers working in concert. Network monitoring forms the foundation, with security operations centers tracking traffic patterns and identifying anomalies in real-time. Endpoint protection secures individual devices, while email filtering blocks phishing attempts before they reach users. Vulnerability management identifies and patches system weaknesses, and incident response protocols ensure swift action when threats materialize.
Core components include:
- 24/7 security monitoring and alerting
- Threat intelligence integration and analysis
- Patch management and vulnerability scanning
- Security information and event management (SIEM)
- Compliance reporting and documentation
- Incident response and forensic investigation
What distinguishes managed IT security from basic IT support is the specialized expertise and dedicated focus on threat prevention. Security landscapes evolve daily, with new attack vectors emerging constantly. Managed providers invest in continuous training, advanced tools, and threat intelligence feeds that would be prohibitively expensive for individual small businesses to maintain independently.
The Business Case for Outsourced Security
Building an in-house security team requires substantial investment. Beyond salaries for qualified professionals, organizations must purchase security tools, maintain certifications, and ensure round-the-clock coverage. For most small businesses, these costs simply don't align with available budgets.
Managed IT security transforms this fixed cost into a predictable operational expense. Providers spread infrastructure and personnel costs across multiple clients, delivering sophisticated capabilities at a fraction of in-house costs. This model democratizes access to enterprise-grade security, putting advanced protection within reach of businesses that couldn't otherwise afford it.
The strategic value extends beyond cost savings. When security experts handle threat management, internal teams focus on revenue-generating activities and core business functions. This productivity gain often exceeds the direct cost savings, as employees concentrate on what they do best rather than wrestling with security complexities they may not fully understand.
| Benefit Category | In-House Security | Managed IT Security |
|---|---|---|
| Initial Investment | $150,000+ annually | $2,000-$5,000 monthly |
| Coverage Hours | Business hours only | 24/7/365 monitoring |
| Expertise Depth | Limited to hired staff | Access to entire security team |
| Tool Licensing | Per-seat, per-tool costs | Included in service fee |
| Scalability | Requires new hires | Instant capacity adjustment |
According to recent industry analysis on managed security services trends, providers increasingly incorporate automation and artificial intelligence to enhance threat detection and response capabilities, delivering more value at competitive price points.
Critical Security Functions Managed Providers Deliver
Modern cyber threats demand multiple specialized capabilities working together. Managed IT security providers orchestrate these functions into a cohesive defense strategy tailored to each client's risk profile and operational requirements.
Continuous Threat Monitoring and Detection
Security operations centers serve as the nerve center for managed protection. Analysts monitor network traffic, system logs, and security alerts across all client environments simultaneously. Advanced correlation engines identify patterns that might indicate compromise, flagging suspicious activities for immediate investigation.
This continuous vigilance catches threats that automated systems might miss. While firewalls and antivirus software block known threats, human analysts recognize behavioral anomalies, social engineering attempts, and zero-day exploits that haven't yet been cataloged. The combination of automation and expertise creates detection capabilities far exceeding what standalone tools provide.
Threat intelligence feeds enhance this monitoring by providing context about emerging attack campaigns, newly discovered vulnerabilities, and indicators of compromise circulating in criminal networks. Managed providers aggregate intelligence from multiple sources, applying relevant insights to protect clients before attacks materialize.
Vulnerability Management and Patch Deployment
Unpatched software represents one of the most common attack vectors. Cybercriminals actively scan for known vulnerabilities, exploiting them before organizations apply available fixes. Managed IT security providers systematically identify, prioritize, and remediate vulnerabilities across client environments.
Regular vulnerability scans assess every device, application, and system component. Results feed into risk-based prioritization frameworks that account for exploit availability, potential impact, and compensating controls. Critical patches deploy quickly through automated systems, while less urgent updates schedule during maintenance windows to minimize business disruption.
The NIST guidelines for secure software development and operations provide frameworks that managed providers implement to ensure comprehensive coverage across development, deployment, and operational phases.
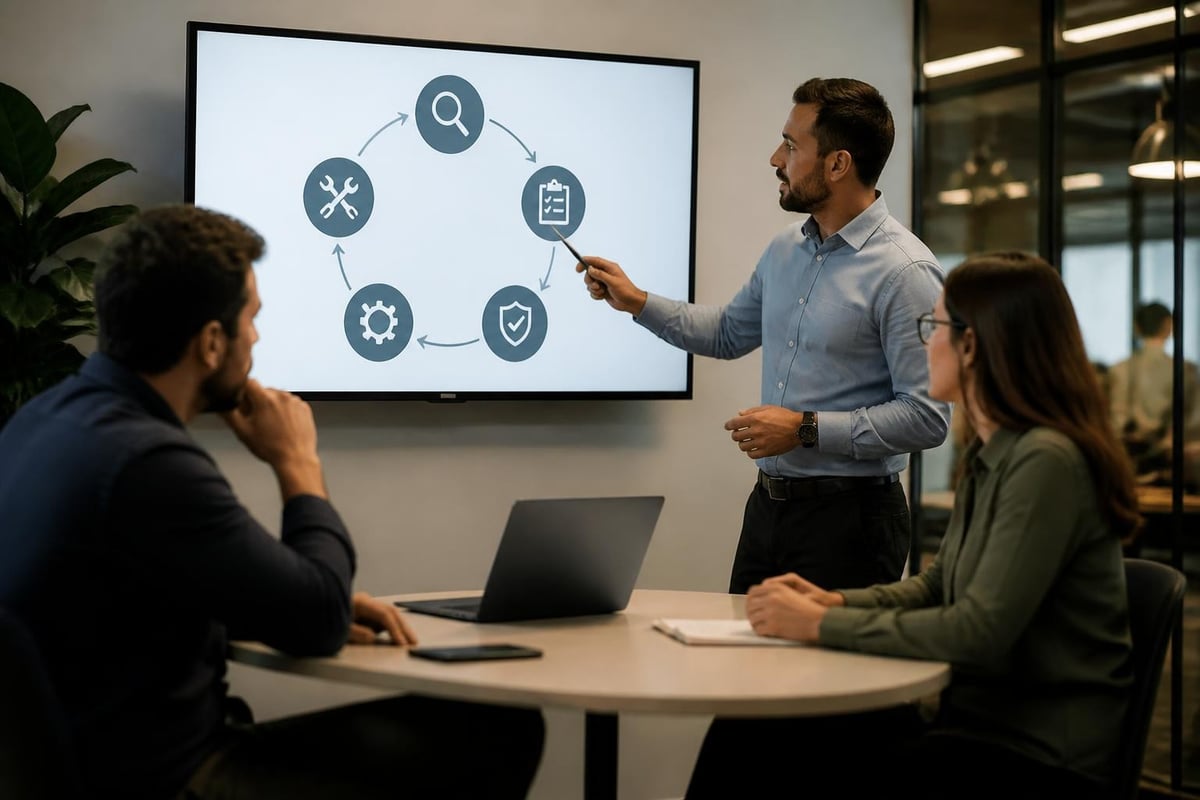
Vulnerability management workflow includes:
- Automated scanning across all network assets
- Risk scoring based on exploitability and business impact
- Prioritized remediation scheduling
- Automated patch testing in isolated environments
- Controlled deployment with rollback capabilities
- Verification scanning to confirm successful remediation
Incident Response and Recovery
Despite best prevention efforts, security incidents occasionally occur. Response speed and effectiveness determine whether an incident becomes a minor disruption or a catastrophic breach. Managed IT security providers maintain documented response protocols activated immediately when threats materialize.
Response teams follow structured methodologies that contain threats, preserve evidence, eliminate attacker presence, and restore normal operations. Clear communication protocols keep business leaders informed throughout the incident, while technical teams execute remediation steps. Post-incident analysis identifies root causes and implements controls to prevent recurrence.
The SANS approach to Continuous Threat Exposure Management emphasizes proactive posture assessment rather than purely reactive response, helping organizations understand their exposure before attackers exploit it.
Evaluating Managed IT Security Providers
Selecting the right provider requires careful assessment of capabilities, experience, and cultural fit. Not all managed security services deliver equal value, and the wrong choice can leave dangerous gaps in protection.
Technical Capabilities and Tool Stack
Examine the specific technologies providers use to deliver protection. Modern managed IT security requires sophisticated platforms for threat detection, security information management, endpoint protection, and network analysis. Leading providers invest continuously in their tool portfolios, ensuring clients benefit from current capabilities.
Ask detailed questions about monitoring coverage, alert investigation procedures, and response timeframes. How quickly do analysts investigate alerts? What triggers escalation to senior security specialists? How does the provider handle threats outside normal business hours? These operational details reveal how protection functions in practice.
Integration capabilities matter significantly. Security tools must connect with existing business systems, cloud platforms, and communication channels. Providers should demonstrate experience with your specific technology stack and explain how they'll adapt their services to your environment rather than forcing you into their predetermined model.
Service Level Agreements and Shared Responsibility
Clear contractual terms prevent misunderstandings about security responsibilities. The CISA guidance on risk considerations for managed service provider customers outlines essential contract elements including response timeframes, reporting requirements, and delineated responsibilities.
Service level agreements should specify measurable commitments for alert response times, patch deployment schedules, report delivery, and availability guarantees. Understand exactly what the provider monitors, what remains your responsibility, and how handoffs occur during incidents.
The shared responsibility model defines which security functions the provider handles versus which remain with internal teams. Clarifying these boundaries prevents dangerous assumptions where each party believes the other is handling a critical function, leaving it completely unaddressed.
| Security Function | Provider Responsibility | Client Responsibility |
|---|---|---|
| Network Monitoring | 24/7 traffic analysis and alerting | Provide network access and credentials |
| Patch Management | Test, deploy, and verify patches | Approve maintenance windows |
| User Training | Provide security awareness materials | Ensure employee participation |
| Access Control | Monitor for suspicious access patterns | Define user permissions and roles |
| Data Backup | Manage backup infrastructure | Identify critical data and retention requirements |
Compliance and Regulatory Expertise
Many industries face specific regulatory requirements governing data protection and security practices. Healthcare organizations must comply with privacy regulations, financial services face stringent data security mandates, and businesses handling payment cards must maintain PCI DSS compliance.
Managed IT security providers familiar with your industry's requirements deliver tremendous value by implementing appropriate controls and generating compliance documentation. They understand which security measures satisfy regulatory obligations and can translate technical implementations into audit-ready reports.
Ask providers about their experience with your specific regulatory environment. Request examples of compliance reports they've produced and references from clients in similar industries. The Forrester Wave report on managed detection and response services evaluates providers partly on their compliance support capabilities, recognizing this as a critical differentiator.
Implementation Considerations for Small Businesses
Successfully deploying managed IT security requires thoughtful planning and realistic expectations. The transition from self-managed or minimal security to comprehensive protection involves technical changes, process adjustments, and cultural shifts.
Initial Assessment and Risk Prioritization
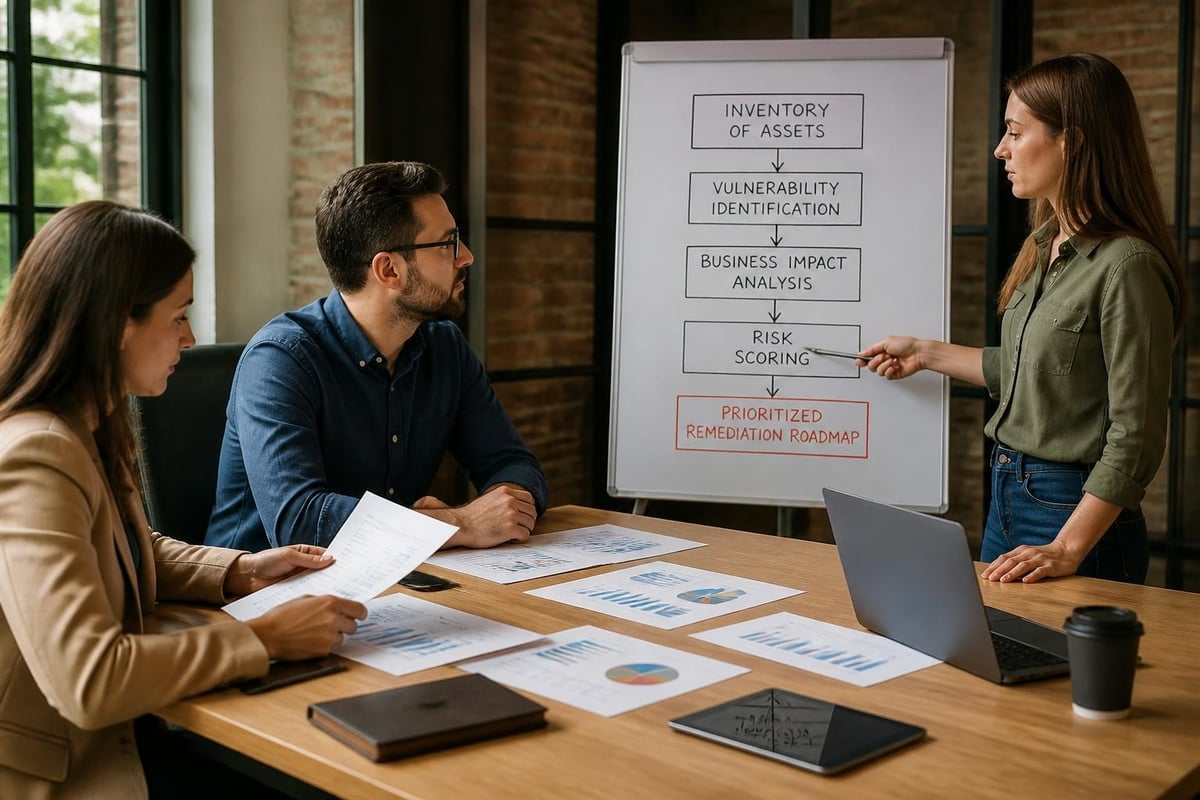
Quality providers begin with thorough security assessments before proposing specific services. This discovery phase examines current infrastructure, identifies existing vulnerabilities, evaluates security controls, and documents business requirements. The assessment creates a baseline understanding of your security posture and risk exposure.
Be prepared for uncomfortable findings. Most small businesses discover significant vulnerabilities during initial assessments. These discoveries aren't criticisms but opportunities for improvement. Providers should present findings constructively, prioritizing risks by potential business impact rather than overwhelming you with every technical detail.
Risk prioritization helps allocate limited budgets effectively. Not every vulnerability demands immediate remediation, and not every control provides equal protection value. Work with your provider to address high-impact risks first, creating a roadmap for progressive security improvement over time.
Onboarding and Integration Timeline
Expect implementation to take several weeks. Providers need time to deploy monitoring agents, configure security tools, establish baseline traffic patterns, and integrate with existing systems. Rushing implementation often creates gaps or disruptions that undermine the security improvements you're trying to achieve.
During onboarding, maintain open communication with your provider. They'll need information about your business processes, critical applications, authorized software, and normal operational patterns. The more context you provide, the better they can tune security controls to minimize false alerts while catching genuine threats.
Plan for some initial adjustment as systems learn your environment and analysts become familiar with your operations. Early days typically generate more alerts as monitoring systems establish normal baselines. Providers should actively tune detection rules during this period, reducing noise while maintaining security effectiveness.
Ongoing Collaboration and Communication
Managed IT security works best as a partnership rather than a completely hands-off outsourcing arrangement. Providers need your input about business changes, new applications, and evolving operational requirements. You need their insights about emerging threats, recommended security improvements, and industry trends.
Establish regular communication cadences that fit your organization's needs. Monthly security briefings review threat landscape developments, discuss detected incidents, and align on upcoming initiatives. Quarterly business reviews assess service delivery, review metrics, and adjust security strategies as your business evolves.
Designate an internal point of contact who understands both your business operations and basic technical concepts. This liaison bridges communication between the managed provider and your organization, ensuring security recommendations translate into practical business decisions.
Strategic Value Beyond Technical Protection
While threat prevention represents the primary value of managed IT security, additional benefits often prove equally important for small business success. These strategic advantages compound over time, creating competitive differentiation beyond immediate security improvements.
Business Continuity and Operational Resilience
Security incidents disrupt operations, sometimes for extended periods. Ransomware attacks can paralyze entire organizations for days or weeks. Data breaches trigger investigation processes that divert resources from productive work. Even unsuccessful attacks create distraction and stress that impact performance.
Managed IT security minimizes these disruptions by preventing most incidents and containing those that occur. Quick detection and response limit attacker dwell time, reducing potential damage. Established recovery procedures restore operations faster when incidents do cause outages. This resilience protects revenue, preserves customer relationships, and maintains employee productivity.
The operational stability managed providers deliver enables better business planning. When security becomes predictable rather than crisis-driven, leadership can focus on growth initiatives, market opportunities, and strategic investments rather than constantly firefighting security emergencies.
Cyber Insurance and Risk Transfer
Insurance providers increasingly require documented security controls before issuing cyber liability policies. Some insurers mandate specific protections, while others adjust premiums based on security maturity. Managed IT security helps satisfy these requirements, often reducing insurance costs or expanding available coverage.
Providers document their security activities, creating the evidence insurers require during underwriting and claims processes. Regular reports demonstrate continuous monitoring, vulnerability management, and incident response capabilities. This documentation proves you've exercised reasonable care protecting sensitive data and systems.
When incidents occur despite security measures, documented controls support insurance claims by showing you maintained appropriate protections. The GIAC paper on outsourcing security management discusses how proper oversight of outsourced security functions contributes to overall risk management frameworks.
Competitive Advantage in Customer Relationships
Customers increasingly evaluate vendors based on security practices before entering business relationships. Large enterprises often require security attestations, vulnerability scan results, or compliance certifications from smaller partners. Demonstrating robust security posture through managed IT security opens opportunities that would otherwise remain inaccessible.
Security becomes a sales differentiator when competitors lack comparable protections. Being able to discuss your monitoring capabilities, incident response procedures, and compliance support during sales conversations builds customer confidence. In industries where data security directly impacts customer trust, managed protection transforms from cost center to revenue enabler.
The SANS cloud service provider management policy template demonstrates the governance frameworks larger organizations expect from their vendors, including those using managed services for security delivery.
Maximizing Return on Managed Security Investment
Getting full value from managed IT security requires active engagement rather than passive consumption. Organizations that treat their provider as a strategic partner realize substantially better outcomes than those viewing security as a commodity service purchased and forgotten.
Leveraging Provider Expertise for Security Education
Use your managed provider as a resource for internal security awareness training. They understand current attack techniques, common vulnerabilities, and effective countermeasures. Many providers offer security training as part of their service packages or can recommend specific focus areas for your employee education programs.
Regular security updates from your provider help staff understand why certain policies exist and how their actions impact organizational security. When employees grasp the reasoning behind security requirements, compliance improves and resistance decreases. Transform security from an obstacle into a shared responsibility everyone understands and supports.
Effective security awareness topics include:
- Recognizing phishing emails and social engineering attempts
- Proper password creation and management practices
- Safe mobile device usage and remote work security
- Incident reporting procedures and escalation paths
- Data handling requirements and privacy obligations
Regular Review and Service Optimization
Schedule periodic reviews examining whether your managed IT security services still align with business needs. As companies grow, technology stacks evolve, and threat landscapes shift, security requirements change accordingly. What worked perfectly two years ago may need adjustment today.
Discuss emerging threats relevant to your industry with your provider. Are new attack techniques targeting businesses like yours? Do regulatory changes require control updates? Should expanding operations into new markets trigger security enhancements? Proactive conversations about evolving needs prevent surprises and ensure continuous protection alignment.
Review security metrics and key performance indicators regularly. Understand what normal looks like for your environment: alert volumes, patch compliance rates, vulnerability counts, and incident frequency. Trending these metrics over time reveals whether security posture is improving, degrading, or holding steady.
Building Internal Capabilities Alongside Managed Services
While managed IT security handles sophisticated threat management, maintaining basic internal security knowledge remains valuable. Staff should understand security fundamentals, recognize obvious threats, and know when to escalate concerns to the managed provider.
Develop internal documentation covering your specific security policies, approved software, data handling procedures, and incident reporting processes. Your managed provider focuses on technical protection; you must ensure employees understand and follow organizational security policies that govern daily activities.
Consider managed IT security a foundation enabling internal capability development rather than a complete replacement for security awareness. The provider handles technical complexity while you maintain ownership of business processes, risk decisions, and strategic security direction.
Managed IT security transforms cybersecurity from an overwhelming technical challenge into a manageable business function, delivering enterprise-grade protection at small business prices. By partnering with specialists who monitor threats continuously, respond to incidents rapidly, and maintain security infrastructure proactively, organizations gain both protection and peace of mind. Delphi Systems Inc. provides comprehensive managed IT services including robust cybersecurity to small businesses throughout Lethbridge and surrounding areas, combining local expertise with advanced security capabilities to keep your operations running smoothly and securely.
