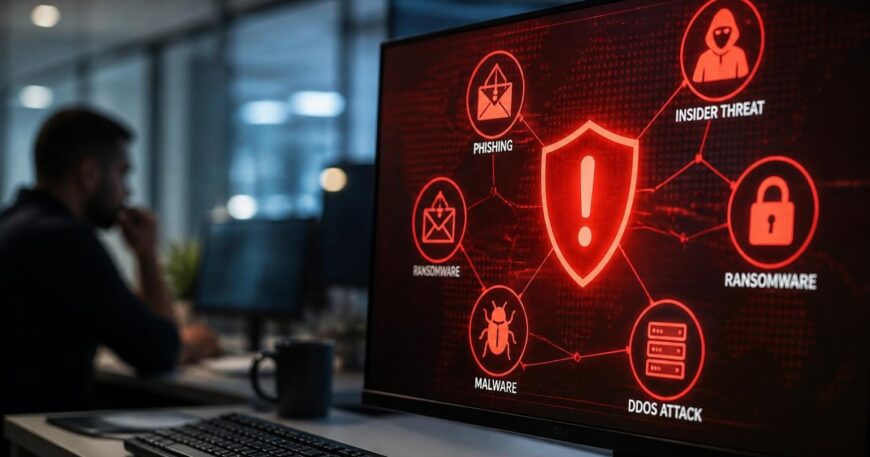
Small businesses today face an unprecedented array of digital dangers that can compromise operations, steal sensitive data, and cripple productivity. Understanding network security threats has become essential for organizations of all sizes, particularly those in Lethbridge and similar communities where local businesses increasingly rely on digital infrastructure. The sophistication of modern attacks continues to evolve, making it critical for business owners to recognize vulnerabilities and implement comprehensive protection strategies. This comprehensive guide examines the most pressing threats facing small businesses in 2026 and provides actionable insights for maintaining secure IT environments.
Understanding Modern Network Security Threats
The landscape of network security threats has transformed dramatically over the past few years. What once required significant technical expertise can now be executed by relatively inexperienced attackers using readily available tools. Cybercriminals have industrialized their operations, creating marketplaces where malicious software and attack services are bought and sold like legitimate products.
Small businesses represent particularly attractive targets because they often lack the robust security infrastructure of larger enterprises while still maintaining valuable data and financial resources. According to recent analyses of the biggest cyber threats businesses face in 2026, attackers increasingly leverage artificial intelligence to enhance their capabilities and scale their operations.
The Economics Behind Cybercrime
Understanding why network security threats proliferate helps businesses take them seriously:
- High return on investment for attackers with minimal physical risk
- Low barriers to entry through ransomware-as-a-service platforms
- Abundant targets among under-protected small business networks
- Cryptocurrency payment methods that obscure financial trails
- International jurisdictions that complicate law enforcement efforts
The professionalization of cybercrime means that defending against network security threats requires equally professional approaches to security.
Malware and Ransomware Attacks
Malicious software remains one of the most pervasive network security threats facing organizations today. Ransomware specifically has evolved into a devastating weapon that encrypts business data and demands payment for its release. These attacks can halt operations entirely, forcing businesses offline for days or even weeks.
Modern ransomware operators employ double-extortion tactics. They not only encrypt data but also exfiltrate it, threatening to publish sensitive information if ransom demands aren't met. This creates reputational and regulatory compliance risks beyond simple operational disruption.
| Malware Type | Primary Impact | Common Entry Points | Average Recovery Cost |
|---|---|---|---|
| Ransomware | Data encryption, operational shutdown | Email attachments, compromised credentials | $50,000-$500,000 |
| Trojans | Backdoor access, data theft | Software downloads, email links | $10,000-$100,000 |
| Spyware | Information stealing, surveillance | Browser vulnerabilities, bundled software | $5,000-$75,000 |
| Worms | Network propagation, resource consumption | Unpatched systems, network shares | $15,000-$150,000 |
Prevention requires a multi-layered approach. Endpoint protection software provides the first line of defense, but businesses must also implement regular backup protocols, employee training, and network segmentation to contain potential infections.
Recognizing Infection Indicators
Early detection significantly improves outcomes when dealing with malware-based network security threats:
- Unusual network traffic patterns or data transfers
- Degraded system performance across multiple devices
- Unexpected file encryption or file extension changes
- Disabled security software or administrative tools
- Unauthorized account access or privilege escalations
Monitoring systems should alert IT teams to these indicators before infections spread throughout the network.
Distributed Denial of Service (DDoS) Attacks
DDoS attacks represent a growing category of network security threats that overwhelm systems with excessive traffic, rendering them unavailable to legitimate users. While large enterprises typically face these attacks, small businesses increasingly encounter them, particularly those with public-facing services or competitive advantages worth disrupting.
The evolution of AI-powered DDoS attacks has made these threats more sophisticated and harder to defend against. Artificial intelligence allows attackers to adapt their strategies in real-time, circumventing traditional mitigation measures.
Volumetric attacks flood bandwidth with massive amounts of traffic. Protocol attacks exploit weaknesses in network protocols to consume server resources. Application layer attacks target specific web applications, requiring fewer resources while causing significant disruption.
Small businesses should work with internet service providers and security specialists to implement DDoS mitigation strategies. Cloud-based protection services can absorb attack traffic before it reaches business networks, maintaining availability during incidents.
Phishing and Social Engineering
Among all network security threats, social engineering attacks prove particularly effective because they target human psychology rather than technical vulnerabilities. Phishing campaigns trick employees into revealing credentials, downloading malware, or transferring funds through increasingly convincing deception.
Traditional email phishing has been joined by smishing (SMS phishing) and vishing (voice phishing). Attackers research targets through social media and public records, crafting highly personalized messages that bypass suspicion.
Common Social Engineering Tactics
Understanding these methods helps employees recognize network security threats before damage occurs:
- Authority impersonation claiming to be executives, IT staff, or vendors
- Urgency creation demanding immediate action to prevent consequences
- Familiarity exploitation using knowledge of business relationships or projects
- Technical confusion leveraging complex terminology to intimidate targets
- Emotional manipulation triggering fear, curiosity, or helpfulness
Training programs should regularly expose employees to simulated attacks, building recognition skills through practice. Organizations that conduct quarterly phishing simulations report significantly lower successful attack rates than those relying solely on annual training sessions.
Advanced Persistent Threats (APTs)
APTs represent sophisticated network security threats where attackers establish long-term presence within networks, quietly exfiltrating data or preparing for future attacks. Unlike opportunistic threats, APTs target specific organizations with clear objectives, often involving intellectual property theft or competitive intelligence gathering.
These attacks unfold across multiple stages. Initial compromise typically occurs through phishing or exploiting software vulnerabilities. Attackers then establish persistence mechanisms, create backdoors, and gradually expand access while avoiding detection.
Small businesses might assume APTs only target large corporations, but supply chain relationships make them indirect targets. Attackers compromise smaller vendors to access larger partners, making every organization a potential entry point. Understanding common network security threats and protection strategies helps businesses recognize when they might be targeted.
Detection requires continuous network monitoring and behavioral analysis. Normal network activity establishes baselines against which anomalies become visible. Security information and event management (SIEM) systems aggregate logs from across the infrastructure, identifying patterns that indicate compromise.
Insider Threats
Not all network security threats originate externally. Insider threats involve current or former employees, contractors, or business partners who misuse authorized access. These threats prove particularly challenging because insiders already possess legitimate credentials and understand security measures.
Insider threats fall into three categories: malicious insiders intentionally causing harm, negligent insiders making careless mistakes, and compromised insiders whose credentials have been stolen by external attackers.
| Insider Threat Type | Motivation | Warning Signs | Mitigation Strategies |
|---|---|---|---|
| Malicious | Financial gain, revenge, ideology | Accessing unnecessary data, working unusual hours | Principle of least privilege, exit procedures |
| Negligent | Convenience, ignorance | Sharing passwords, bypassing security | Regular training, usability improvements |
| Compromised | N/A (external control) | Unusual login locations, access patterns | Multi-factor authentication, behavior monitoring |
Preventing insider threats requires balancing security with trust. Organizations should implement role-based access controls that limit permissions to only what employees need for their responsibilities. Regular access reviews ensure departing employees lose credentials promptly and role changes trigger appropriate permission updates.
Monitoring solutions track user activity without creating oppressive surveillance environments. Alerts trigger when employees access unusual data volumes, use unfamiliar devices, or exhibit other anomalous behaviors requiring investigation.
Internet of Things (IoT) Vulnerabilities
The proliferation of connected devices introduces new network security threats that many businesses overlook. Security cameras, smart thermostats, printers, and other IoT devices often ship with default credentials and receive infrequent security updates, creating persistent vulnerabilities.
Attackers compromise IoT devices to gain network footholds, launch DDoS attacks, or spy on business activities. A single unsecured device can undermine comprehensive security measures protecting traditional IT infrastructure.
Businesses should inventory all connected devices and isolate them on separate network segments. IoT devices should never share networks with critical business systems. Default passwords must be changed immediately upon deployment, and devices incapable of receiving security updates should be replaced or removed.
IoT Security Best Practices
Implementing these measures reduces exposure to IoT-related network security threats:
- Conduct regular device inventories to track all network-connected equipment
- Segment IoT devices onto isolated network zones with restricted access
- Disable unnecessary features and services on all connected devices
- Monitor IoT device traffic for unusual patterns or communications
- Establish update schedules ensuring devices receive timely security patches
Network access control solutions can prevent unauthorized devices from connecting, while behavior-based monitoring detects compromised devices even when they possess valid credentials.
Man-in-the-Middle Attacks
Man-in-the-middle (MitM) attacks occur when attackers intercept communications between two parties, potentially reading or modifying transmitted data. These network security threats commonly target unsecured Wi-Fi networks, making coffee shops and public spaces particularly dangerous for business activities.
ARP spoofing, DNS hijacking, and SSL stripping represent common MitM techniques. Attackers position themselves between users and legitimate services, capturing credentials, financial data, or sensitive business information.
Virtual private networks (VPNs) encrypt traffic, preventing interception even on compromised networks. Businesses should require VPN usage for all remote work and provide corporate devices configured with automatic VPN connections. Understanding network-level cyberattacks and prevention methods helps organizations implement appropriate countermeasures.
Certificate validation ensures users connect to legitimate services rather than attacker-controlled imposters. Employees should be trained to recognize browser security warnings and never proceed past certificate errors, even when connecting to familiar services.
Zero-Day Exploits
Zero-day exploits target previously unknown software vulnerabilities, giving defenders no time to patch before attacks occur. These network security threats prove particularly dangerous because no signatures or detection patterns exist until after initial exploitation.
Software vendors, security researchers, and attackers race to discover vulnerabilities. When attackers find them first, organizations face exposure until patches become available. Critical vulnerabilities in widely-used software can affect thousands of businesses simultaneously.
Mitigation focuses on defense-in-depth strategies that contain breaches even when prevention fails. Application whitelisting prevents unauthorized software execution. Network segmentation limits lateral movement. Backup systems enable recovery without paying ransoms.
Vulnerability management programs prioritize patching based on risk assessment. Critical systems facing internet exposure receive immediate updates, while less critical systems follow testing protocols ensuring patches don't disrupt operations.
Establishing Comprehensive Protection
Defending against network security threats requires integrated strategies combining technology, processes, and people. No single solution provides complete protection, making layered defenses essential for small business security.
Firewall configurations control network traffic based on security rules. Intrusion detection systems monitor for attack signatures and anomalous behaviors. Email filtering blocks malicious messages before reaching users. Endpoint protection prevents malware execution on individual devices.
Regular security assessments identify vulnerabilities before attackers exploit them. Penetration testing simulates real attacks, revealing weaknesses in technical controls and employee awareness. Vulnerability scanning automates the discovery of misconfigurations and missing patches across the infrastructure.
Essential Security Components
Building robust defenses against network security threats requires these foundational elements:
- Next-generation firewalls with deep packet inspection and application awareness
- Endpoint detection and response providing visibility across all devices
- Email security gateways filtering phishing attempts and malicious attachments
- Network access control authenticating and authorizing device connections
- Security information and event management aggregating logs for analysis
- Data backup and recovery enabling restoration after ransomware or disasters
Professional managed services provide expertise and monitoring capabilities beyond most small business budgets for internal teams. Comprehensive resources about network security threats and protective strategies help businesses understand what protection measures address which risks.
Employee Training and Awareness
Technology alone cannot defend against network security threats that exploit human psychology. Security awareness training transforms employees from vulnerabilities into defensive assets who recognize and report suspicious activities.
Effective training programs deliver regular, engaging content that employees actually remember. Monthly security tips, quarterly simulated phishing exercises, and annual comprehensive training create continuous reinforcement rather than once-yearly information dumps quickly forgotten.
Training should address specific threats employees encounter: recognizing phishing emails, securing mobile devices, protecting credentials, and reporting incidents. Real-world examples from similar businesses make threats tangible rather than abstract.
Creating a security-conscious culture requires leadership commitment. When executives visibly prioritize security, employees understand its importance. Positive reinforcement for employees who report suspicious emails proves more effective than punishment for those who fall for simulations.
Incident Response Planning
Despite best efforts, some network security threats will succeed. Incident response plans minimize damage through coordinated, rehearsed procedures activated immediately upon detection.
Response plans define roles, establish communication channels, and outline containment procedures. Technical teams isolate affected systems. Management teams assess business impact and make operational decisions. Communications teams coordinate with customers, partners, and potentially regulators.
Regular tabletop exercises test plans without requiring actual incidents. Teams work through realistic scenarios, identifying gaps in procedures or resources. These exercises build muscle memory so teams respond effectively under stress.
Documentation proves critical for both response and recovery. Teams should record timeline details, actions taken, and lessons learned. This information supports forensic investigation, insurance claims, and process improvements preventing recurrence.
Regulatory Compliance Considerations
Many industries impose specific security requirements that businesses must meet. Healthcare organizations face HIPAA regulations. Financial services comply with PCI-DSS for payment card data. Canadian businesses handling personal information must follow PIPEDA requirements.
Compliance frameworks address common network security threats through mandated controls. Regular risk assessments, access controls, encryption, and audit logging appear across most regulations. Meeting compliance requirements simultaneously improves security posture.
Non-compliance risks extend beyond network security threats themselves. Regulatory violations trigger fines, lawsuits, and reputational damage that can exceed breach costs. Documenting security measures and maintaining evidence of compliance prove essential during audits or incident investigations.
Emerging Threats on the Horizon
The threat landscape continues evolving as attackers adopt new technologies and techniques. Artificial intelligence enhances phishing campaigns with generated content indistinguishable from legitimate communications. Quantum computing threatens current encryption methods, requiring preparation for post-quantum cryptography.
Supply chain attacks compromise software development processes, inserting malicious code into legitimate applications. Businesses must evaluate vendor security practices and implement controls for third-party software. Resources examining top network security threats and protective measures provide insights into evolving attack methods.
Cloud adoption introduces new network security threats as business data moves beyond traditional perimeter defenses. Misconfigured cloud storage, compromised API credentials, and insufficient access controls create exposures that attackers actively seek.
Staying informed about emerging threats allows businesses to adapt defenses proactively. Security news sources, vendor notifications, and professional associations provide threat intelligence that informs strategic planning and tactical responses.
Network security threats continue growing in sophistication and frequency, making professional protection essential for small businesses that cannot afford dedicated security teams. Understanding the threats facing your organization represents the first step toward building effective defenses that protect operations, data, and reputation. Delphi Systems Inc. provides comprehensive managed IT services including cybersecurity, network monitoring, and data backup specifically designed for small businesses in Lethbridge and surrounding areas, delivering enterprise-grade protection through fixed-rate services that let you focus on running your business while we maintain your security.

