A cyber network forms the backbone of modern business operations, connecting devices, systems, and users while enabling the flow of critical information across your organization. For small businesses in Lethbridge and across Canada, understanding how to design, implement, and secure these networks has become essential to maintaining competitive advantage and protecting valuable assets. The complexity of today's cyber network environments, with cloud services, remote workers, and interconnected systems, demands a strategic approach that balances accessibility with robust security measures.
Understanding Modern Cyber Network Architecture
The foundation of any effective cyber network begins with solid architectural principles that support both current operations and future growth. Unlike traditional networks that operated within clearly defined perimeters, today's cyber network infrastructure extends across multiple locations, cloud platforms, and mobile devices.
Network design principles have evolved significantly to address contemporary challenges:
- Scalability ensures your cyber network can accommodate business growth without complete redesigns
- Redundancy provides failover capabilities that maintain operations during hardware failures or attacks
- Segmentation isolates critical systems and limits the spread of potential security breaches
- Flexibility allows integration of new technologies and services as business needs change
These foundational elements create a resilient framework that supports business continuity. When properly implemented, network design principles enable organizations to adapt quickly to changing market conditions while maintaining security and performance standards.
Building Blocks of Cyber Network Infrastructure
Every cyber network consists of interconnected components that work together to facilitate communication and data exchange. The physical layer includes routers, switches, firewalls, and cabling that provide the actual pathways for data transmission. Above this sits the logical layer, where IP addressing, VLANs, and routing protocols determine how information flows between systems.
For small businesses, the challenge often lies in balancing comprehensive coverage with budget constraints. Cloud-based solutions have democratized access to enterprise-grade cyber network capabilities, allowing smaller organizations to leverage infrastructure that would have been prohibitively expensive just a few years ago.
| Network Component | Primary Function | Security Consideration |
|---|---|---|
| Firewalls | Traffic filtering and access control | Regular rule updates and monitoring |
| Switches | Device connectivity and data forwarding | VLAN configuration and port security |
| Routers | Network interconnection and path determination | Firmware updates and access restrictions |
| Wireless Access Points | Mobile device connectivity | Strong encryption and authentication |
| VPN Gateways | Secure remote access | Multi-factor authentication requirements |
Cyber Network Security Fundamentals
Protecting your cyber network requires a multi-layered approach that addresses threats at every level. The days of relying solely on perimeter defenses have passed, as modern threats often originate from within networks or exploit legitimate access credentials.
The zero-trust security model has emerged as the gold standard for cyber network protection. This framework assumes that no user or device should be trusted by default, regardless of whether they're inside or outside the network perimeter. Every access request must be verified, authenticated, and authorized based on multiple factors.
Implementing Layered Defense Strategies
Defense in depth creates multiple barriers that attackers must overcome to compromise your cyber network. This approach recognizes that no single security measure is foolproof, so overlapping protections provide redundancy and increase the likelihood of detecting and stopping threats.
Essential security layers include:
- Perimeter security through firewalls and intrusion prevention systems
- Network segmentation that isolates sensitive data and critical systems
- Access controls enforcing the principle of least privilege
- Encryption protecting data in transit and at rest
- Monitoring and logging providing visibility into network activity
- Incident response procedures enabling rapid threat containment
Organizations implementing network security best practices create resilient environments that can withstand sophisticated attacks. The key is consistency in application and regular updates to address emerging threats.
Managing Network Access and Authentication
Controlling who and what can access your cyber network represents one of the most critical security functions. Weak authentication mechanisms continue to be exploited by attackers seeking unauthorized entry points.
Modern access management goes beyond simple username and password combinations. Multi-factor authentication (MFA) requires users to provide multiple forms of verification, significantly reducing the risk of credential-based attacks. Biometric authentication, hardware tokens, and one-time codes add layers of verification that make unauthorized access exponentially more difficult.
Network access control (NAC) systems examine devices attempting to connect to your cyber network, verifying their security posture before granting access. These systems can check for current antivirus definitions, operating system patches, and compliance with organizational security policies. Non-compliant devices can be quarantined or granted limited access until they meet security requirements.
Protecting Against Contemporary Threats
The threat landscape facing cyber network administrators in 2026 is more sophisticated than ever. Attackers employ advanced techniques including artificial intelligence, polymorphic malware, and social engineering to circumvent traditional defenses.
Ransomware attacks have evolved from opportunistic infections to targeted campaigns against specific organizations. These attacks often begin with reconnaissance of the target cyber network, identifying valuable data and critical systems. Attackers then establish persistent access, moving laterally through the network until they can encrypt essential resources and demand payment.
| Threat Type | Attack Vector | Mitigation Strategy |
|---|---|---|
| Ransomware | Email phishing, vulnerable services | Regular backups, patch management, email filtering |
| DDoS Attacks | Traffic flooding | Traffic shaping, cloud-based protection, redundancy |
| Insider Threats | Legitimate access abuse | Activity monitoring, data loss prevention, access reviews |
| Zero-Day Exploits | Unpatched vulnerabilities | Intrusion detection, network segmentation, threat intelligence |
| Supply Chain Attacks | Third-party compromise | Vendor assessment, isolated environments, monitoring |
The importance of continuous cybersecurity training cannot be overstated. Human error remains a significant factor in successful cyber network breaches, making employee education a critical component of any security program.
Monitoring and Threat Detection
Visibility into cyber network activity enables early detection of suspicious behavior and rapid response to security incidents. Security Information and Event Management (SIEM) systems aggregate logs from across your infrastructure, correlating events to identify potential threats.
Behavioral analytics add another dimension to threat detection by establishing baseline patterns for normal network activity. Deviations from these baselines trigger alerts that security teams can investigate. This approach is particularly effective at identifying insider threats and compromised credentials that might otherwise appear legitimate.
Advanced cyber network monitoring incorporates:
- Real-time traffic analysis identifying anomalous patterns
- Endpoint detection and response monitoring individual devices for suspicious activity
- Vulnerability scanning proactively identifying security weaknesses
- Threat intelligence integration leveraging global data on emerging threats
- Automated response capabilities containing threats before they spread
Small businesses often lack dedicated security operations centers, making managed detection and response services an attractive option. These services provide expert monitoring and incident response without requiring significant internal resources.
Cyber Network Compliance and Governance
Regulatory requirements increasingly mandate specific cyber network security controls and practices. Organizations handling personal information must comply with privacy regulations, while those in specific industries face additional sector-specific requirements.
Documentation plays a crucial role in demonstrating compliance and due diligence. Maintaining current network diagrams, security policies, access control lists, and change management records provides evidence of responsible network management. This documentation also proves invaluable during incident response and recovery operations.
Risk Assessment and Management
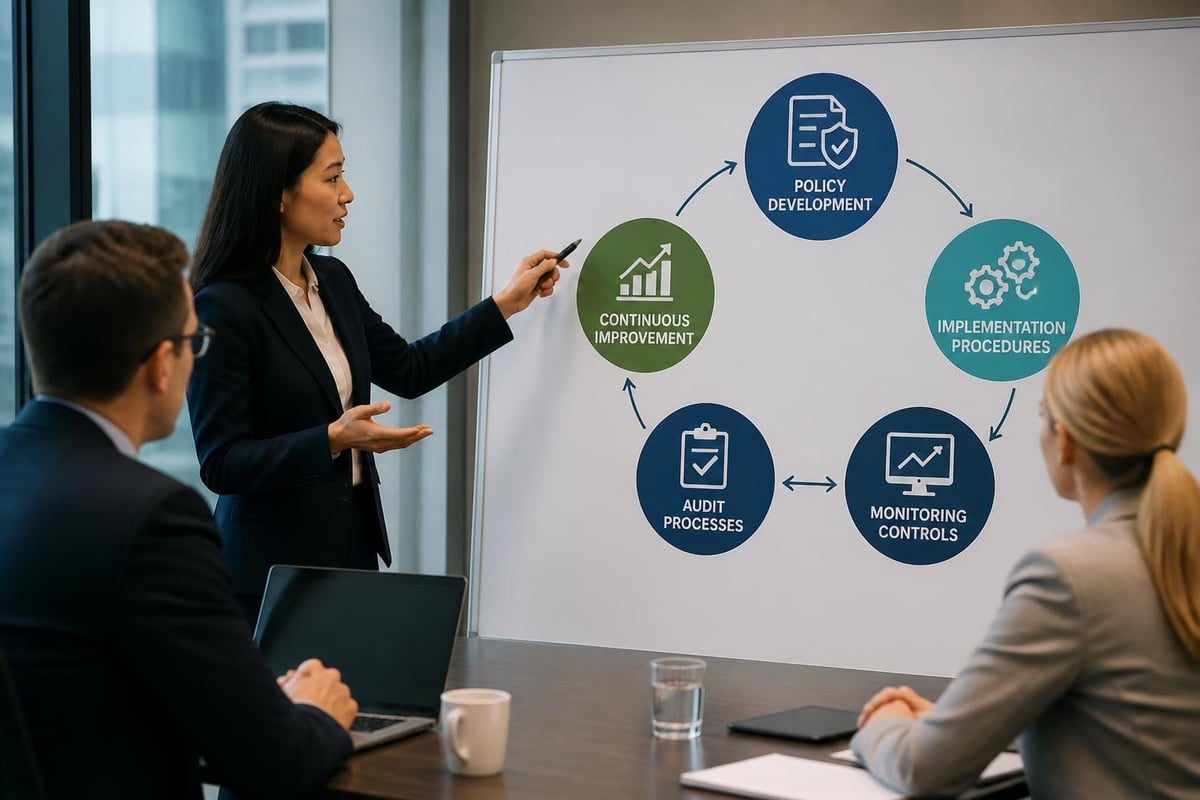
Understanding the risks facing your cyber network enables informed decisions about security investments and priorities. Risk assessments identify assets, evaluate threats, determine vulnerabilities, and calculate potential impacts.
Effective risk management follows a structured process:
- Asset identification cataloging all cyber network components and data
- Threat analysis determining what could go wrong and how
- Vulnerability assessment identifying weaknesses that threats could exploit
- Impact evaluation calculating potential damage from successful attacks
- Control selection choosing appropriate safeguards based on risk levels
- Implementation deploying selected controls across the cyber network
- Monitoring tracking control effectiveness and emerging risks
The evolving landscape of cyber insurance requires organizations to demonstrate robust security practices. Insurers increasingly demand evidence of comprehensive cyber network protection before issuing policies or processing claims.
Best Practices for Cyber Network Maintenance
Maintaining peak cyber network performance requires ongoing attention and regular updates. Reactive approaches that only address problems after they occur inevitably lead to downtime, security breaches, and productivity losses.
Proactive maintenance schedules should include regular tasks that keep your cyber network running smoothly. Firmware updates for network devices patch security vulnerabilities and add new features. Performance monitoring identifies bottlenecks before they impact users. Capacity planning ensures infrastructure scales appropriately with business growth.
The National Cyber Security Centre’s guidance emphasizes the importance of understanding your network's assets and potential threats as foundational steps in maintaining security.
Patch Management and Update Procedures
Unpatched systems represent one of the most common vulnerabilities in cyber network environments. Attackers actively scan for known vulnerabilities, exploiting them before organizations can apply available patches.
Effective patch management balances the need for security updates with operational stability. Testing patches in non-production environments before widespread deployment helps identify potential compatibility issues. Prioritizing critical security patches ensures the most dangerous vulnerabilities receive immediate attention.
Automated patch management tools provide several advantages:
- Centralized visibility into patch status across the cyber network
- Scheduled deployment windows that minimize business disruption
- Rollback capabilities if patches cause unexpected issues
- Compliance reporting demonstrating timely patch application
- Reduced administrative overhead through automation
Organizations implementing comprehensive cybersecurity best practices create resilient cyber network environments that protect against known and emerging threats.
Cloud Integration and Hybrid Environments
Modern cyber network architectures increasingly incorporate cloud services alongside traditional on-premise infrastructure. This hybrid approach provides flexibility and scalability while introducing new security considerations.
Cloud connectivity extends your cyber network beyond physical boundaries, requiring careful attention to secure communication channels. Virtual private networks, dedicated connections, and encrypted tunnels protect data traversing public internet infrastructure. Identity and access management becomes more complex when users access resources across multiple platforms.
| Deployment Model | Characteristics | Security Considerations |
|---|---|---|
| On-Premise | Full control, physical security | Hardware maintenance, scalability limits |
| Public Cloud | Scalability, reduced maintenance | Shared responsibility model, data sovereignty |
| Private Cloud | Dedicated resources, customization | Higher costs, management complexity |
| Hybrid | Flexibility, workload optimization | Integration complexity, consistent policies |
The shared responsibility model in cloud environments divides security obligations between providers and customers. Cloud providers secure the underlying infrastructure, while customers remain responsible for configuring services securely and protecting their data. Understanding these boundaries prevents security gaps in your cyber network.
Software-Defined Networking
Software-defined networking (SDN) separates the control plane from the data plane, enabling programmatic management of cyber network resources. This approach provides unprecedented flexibility in configuring and optimizing network behavior.
SDN controllers provide centralized visibility and control across distributed cyber network infrastructure. Administrators can implement policy changes network-wide through software interfaces rather than configuring individual devices. This centralization simplifies management while enabling rapid response to changing requirements.
Network virtualization through SDN creates logical networks that operate independently on shared physical infrastructure. This capability supports multi-tenancy, testing environments, and rapid deployment of new services without hardware changes.
Building Cyber Network Resilience
Resilience encompasses the ability to withstand attacks, maintain operations during incidents, and recover quickly from disruptions. A resilient cyber network doesn't just prevent breaches but also limits their impact and enables rapid restoration of normal operations.
Business continuity planning identifies critical functions and establishes procedures for maintaining them during various disruption scenarios. Disaster recovery plans specifically address cyber network restoration, including backup systems, alternate communication paths, and recovery time objectives.
Key resilience components include:
- Redundant infrastructure eliminating single points of failure
- Geographic distribution protecting against localized disasters
- Automated failover maintaining service continuity without manual intervention
- Regular testing validating that backup systems function as designed
- Documentation providing clear procedures for recovery operations
The academic research on cyber resilience in next-generation networks explores advanced approaches to building networks that can adapt to and recover from sophisticated attacks.
Backup and Recovery Strategies
Data backup represents the last line of defense against ransomware, hardware failures, and accidental deletion. A comprehensive backup strategy protects not just data but also system configurations, applications, and network settings.
The 3-2-1 backup rule provides a simple framework: maintain three copies of data, on two different media types, with one copy stored off-site. This approach protects against various failure scenarios, from local disasters to ransomware encryption.
Regular testing of recovery procedures validates that backups are usable and that restoration processes work as expected. Many organizations discover backup failures only when attempting recovery during actual emergencies. Scheduled recovery drills identify and correct issues before they become critical.
Future-Proofing Your Cyber Network
Technology evolution continues accelerating, requiring cyber network architectures that can adapt to emerging trends and threats. Planning for the future involves balancing current needs with anticipated developments.
The proliferation of Internet of Things (IoT) devices introduces new endpoints to cyber network environments. These devices often have limited security capabilities, making them attractive targets for attackers. Network segmentation isolates IoT devices, preventing them from providing access to critical systems.
Artificial intelligence and machine learning increasingly play roles in both cyber network management and security. These technologies analyze vast amounts of data to identify patterns, predict issues, and automate responses. However, attackers also leverage AI, creating an ongoing arms race.
5G networks and edge computing push processing closer to data sources, reducing latency while distributing cyber network infrastructure. These architectures require security controls that operate effectively in distributed environments without centralized choke points.
Zero-trust architecture principles will continue gaining adoption as traditional perimeter-based security proves inadequate. The best practices for implementing zero-trust models emphasize continuous verification and least-privilege access across all cyber network resources.
Preparing for Quantum Computing
Quantum computing threatens current encryption standards that protect cyber network communications and stored data. While practical quantum computers capable of breaking widely-used encryption remain years away, organizations should begin preparing for this transition.
Post-quantum cryptography develops encryption algorithms resistant to quantum attacks. Standards organizations are currently evaluating and selecting these algorithms for future adoption. Transitioning to quantum-resistant encryption will require significant cyber network infrastructure updates.
Crypto-agility, the ability to quickly switch encryption algorithms, will become increasingly important. Designing systems with replaceable cryptographic components enables rapid updates when new threats emerge or standards change.
Building and maintaining a secure, efficient cyber network requires expertise, ongoing attention, and strategic planning that many small businesses struggle to provide internally. The complexities of modern network architecture, evolving threats, and compliance requirements demand specialized knowledge and continuous monitoring. Delphi Systems Inc. delivers comprehensive managed IT services designed specifically for small businesses in Lethbridge and surrounding areas, providing the network monitoring, cybersecurity, and proactive maintenance that keep your operations running smoothly while you focus on growing your business.

